
Home › Our Services › Managed Detection, Intelligence & Response
Complete threat coverage. No alert left untriaged.
Round-the-clock detection and response across your entire attack surface. Longwall combines global SOC capability with analysts who understand your environment – ensuring every alert is handled, threats are contained quickly, and your security improves over time.
WHAT THIS SERVICE DELIVERS
Complete visibility. Faster response.
Longwall extends managed detection beyond traditional SOC coverage. Our analysts investigate third-party, custom and contextual alerts alongside your core security telemetry – giving you continuous protection, faster response and confidence that nothing important is left unhandled.
Every alert handled
We monitor and triage alerts across your security environment 24/7/365 – including third-party, custom and contextual data sources. Signals are correlated and tuned to your organisation so genuine threats are surfaced quickly and alert noise is reduced.
Greater context
Threat intelligence and contextual knowledge of your environment enrich every investigation. Sector-specific alerting and proactive threat hunting help identify emerging risks and explain what they mean for your organisation.
Faster containment
We monitor and triage alerts across your security environment 24/7/365 – including third-party, custom and contextual data sources. Signals are correlated and tuned to your organisation so genuine threats are surfaced quickly and alert noise is reduced.
Stronger over time
Threat intelligence and contextual knowledge of your environment enrich every investigation. Sector-specific alerting and proactive threat hunting help identify emerging risks and explain what they mean for your organisation.
The challenge
Standard MDR services can still leave critical gaps.
Many organisations have invested in strong detection technology but still lack the capacity, context or specialist expertise to handle every alert. Third-party feeds remain unmonitored, tooling is underused, and internal teams spend too much time managing noise rather than reducing risk.
Alerts are still being left unhandled
Core MDR services do not always cover every third-party, custom or contextual alert. Without the resource to triage them internally, important activity can be delayed or missed altogether.
Internal teams are overloaded
Alert fatigue, skills gaps and competing priorities limit the time available for tuning, investigation and response. Even capable teams can struggle to maintain continuous coverage without additional headcount.
Technology is not being fully utilised
Powerful detection platforms are often underconfigured or disconnected from existing workflows. Custom integrations, event feeds, automation and reporting remain unused – limiting visibility and return on investment.
Coverage drops outside working hours
Cyber threats don’t stop outside business hours. Without continuous monitoring and response, incidents have more time to develop before the right people are available.
how it works
Continuous protection.
From detection to response.
Our Unified Managed Cyber (UMC) service connects data, analysts, intelligence and response – ensuring threats are identified, investigated and resolved with clear ownership from start to finish.
Connect & Ingest
Bring your security data together
We integrate telemetry from your existing security technologies, including third-party and custom event sources, to create comprehensive visibility across your environment.
Detect & Triage
Surface genuine threats
Analytics, automation and analyst-led triage identify suspicious activity, reduce false positives and ensure every relevant alert receives the appropriate level of investigation.
Investigate & Enrich
Understand the full context
Our analysts combine threat intelligence with knowledge of your environment, users and priorities to determine what has happened, which assets are affected and how serious the risk is.
Respond & Contain
Act before threats escalate
Automated workflows and coordinated incident response contain confirmed threats quickly. Longwall Security owns the investigation and works with your team when business-specific action is required.
Tune & Improve
Strengthen detection continuously
Investigation findings are used to refine detection logic, workflows, dashboards and response processes - improving accuracy and operational effectiveness over time.
Operational outcomes
The difference it makes.
Greater threat visibility, faster response and fewer operational gaps – without adding pressure to your internal team.
Telemetry Visibility
Visibility across core, third-party, custom and contextual data sources, ensuring threats can be detected, investigated and responded to wherever they originate.
Security Operations
Continuous monitoring, investigation and response coordination ensures critical threats and escalations are assessed and managed whenever they occur.
Time to Appropriate Response
Effective security operations are not measured by how quickly someone responds to an alert, but how quickly the right decision is made. Every investigation is assessed against organisational context and coordinated accordingly.
Unlimited visibility. No hidden limits.
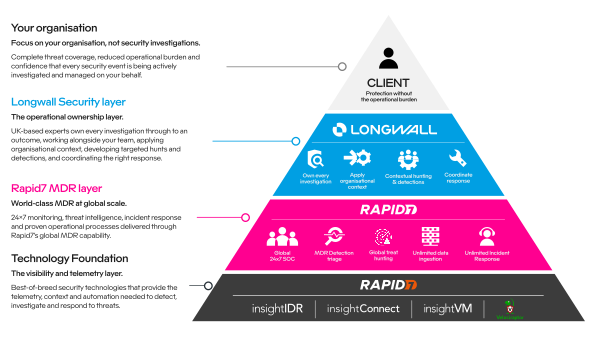
Your visibility shouldn’t be limited by licensing restrictions. Unlike providers that restrict how much telemetry you can ingest, Longwall Security enables unlimited data ingestion – giving your team broader visibility across the environment and greater confidence that relevant threats are detected, investigated and responded to.
Service features
Everything you need to detect and respond.
Integrated technology, continuous analyst coverage and hands-on operational support – delivered through one managed service.
“Longwall Security's expertise has materially improved our security posture and resilience, helping us better understand and manage cyber risk across the organisation.”
Chris Page
Head of Technical Services
Ready for complete threat coverage?
Discover how Longwall Security goes beyond your existing MDR capability with broader visibility, continuous monitoring and expert-led response.